
Blog Articles
Practical articles on AI security, cyber readiness, security operations and the events that matter to security buyers and partners in the Middle East.
Articles
Could a company run without a single employee?
Imagine a company where every role is an AI agent. The technology is easier to picture than the legal, social and philosophical questions.
Read article →
The AI Cost Problem Nobody Talks About: Why AI FinOps Must Become a Boardroom Discussion
AI is becoming an operational budget category. The four pillars of AI FinOps: visibility, optimization, governance and value realization.
Read article →
Why BFSI Leaders in the Middle East Must Act on Post-Quantum Cryptography (PQC) Now—Not Later
Harvest now, decrypt later puts long-retention banking data at risk. A phased PQC readiness journey for Middle East financial institutions.
Read article →
The Five Reasons Organizations Keep Delaying AI Adoption — And What To Do About Them
No chief AI officer, unclear use cases, in-house agent builders, unready data and data-residency limits: five barriers and practical ways past them.
Read article →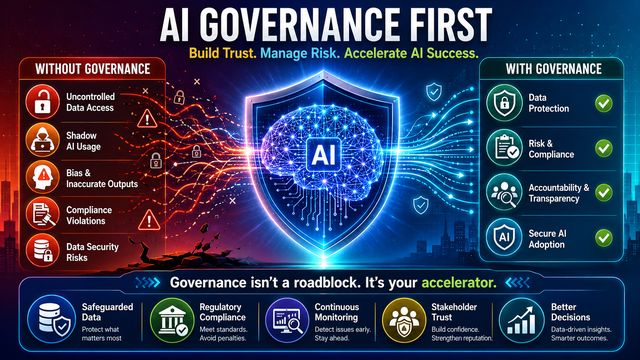
Why AI Governance Must Come Before AI Platforms in the Enterprise
Pick a platform first and governance becomes an afterthought. Why governance must come before AI deployment and how it speeds adoption.
Read article →
Why Management Prefers Human Touch Over AI-Generated Content — And What We’re Missing
AI compresses days of work into minutes, yet leaders distrust unedited output. The case for human signature plus AI acceleration.
Read article →
Claude Mythos & Enterprise Readiness: When Frontier AI Meets Real-World Risk
Frontier AI is entering critical-infrastructure discussions. Why enterprise readiness, not model capability, is now the constraint.
Read article →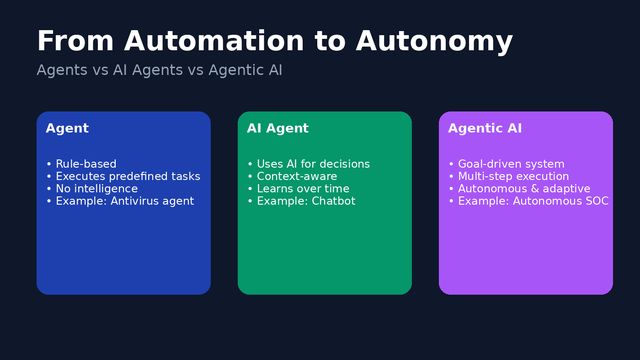
From Automation to Autonomy: Understanding Agents, AI Agents, and Agentic AI
Three terms often used interchangeably but not the same: what each means, where it is used and why it matters for cybersecurity.
Read article →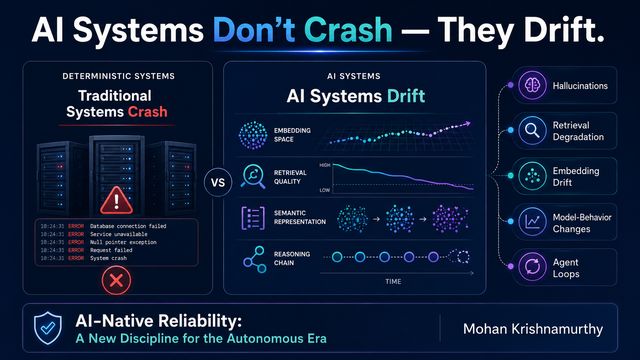
AI Systems Don’t Crash — They Drift. And That Changes Everything.
AI systems fail semantically, not mechanically. Why enterprises need AI-native reliability: SRE for AI, not just AI for SRE.
Read article →
How SBOM Intelligence Can Strengthen Enterprise Cyber Resilience in a Time of Regional Cyber Warfare
Software supply chains are a battleground. How SBOM intelligence turns a static component list into an active layer of defense.
Read article →
Cost-Intelligent AI Adoption: A FinOps-Driven Tri-Modal Strategy
A white paper on a FinOps-driven, tri-modal strategy for scalable, secure and cost-optimized enterprise AI: right workload, right model, right cost.
Read article →
When Computers Came for Jobs... and When AI Came for Everything Else
AI is not only about job loss but about how work is redefined: higher expectations, invisible effort, verification work and adoption friction.
Read article →
Vibe Coding vs. Building a Real Software Business
Why a brilliant idea and fast coding are not enough: what enterprises expect and what a sustainable software company needs.
Read article →
Securing Modern Applications: Why SAST, DAST, and Runtime Security Must Work Together
No single testing method covers a modern application. How SAST, DAST and runtime security complement each other.
Read article →
Why Organizations Should Adopt AI — But Not Run It Themselves
Adopting AI is a strategic decision; running AI infrastructure is an operational burden. The case for AI managed services.
Read article →
How AI Is Influencing the Software Development Lifecycle (SDLC)
AI has not replaced the SDLC but is influencing every stage, from requirements to maintenance, by reducing friction and tightening feedback.
Read article →
When Tech Giants Joined the Party
A light April Fools’ Day roundup of memorable pranks from Google, Apple, Amazon, YouTube and Twitter.
Read article →
Agentic AI: The Cybersecurity Earthquake Reshaping 2026
Autonomous attackers, unmanaged AI agents and identity abuse are reshaping cyber defense. What CISOs and Middle East security leaders should prioritise.
Read article →
5 Simple Tests to Check If Your AI Platform Is Hallucinating
Five quick tests anyone can run to find out whether an AI tool is accurate or just confidently wrong.
Read article →
The AI Tower of Babel: Why Every Cloud Speaks a Different Language — And What It Means for Your Strategy
Azure, Google Cloud and AWS bring three different philosophies to AI. How to read the differences and choose on strengths, not brand.
Read article →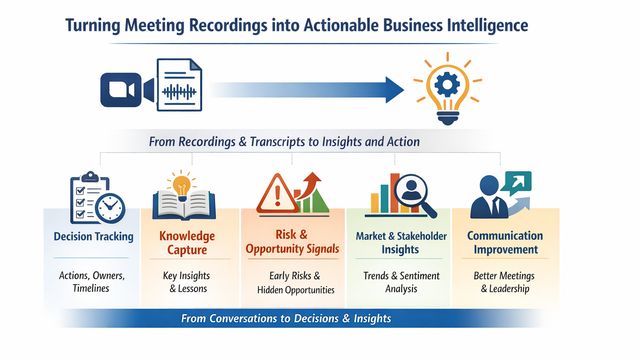
Turning Meeting Recordings into Actionable Business Intelligence
Recordings paired with transcription become a source of operational, strategic and organizational intelligence, not just a reference file.
Read article →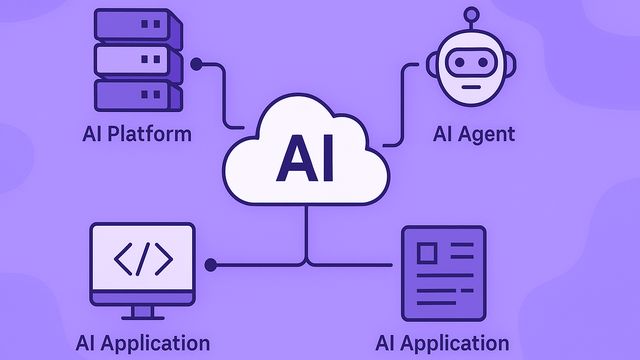
Demystifying Amazon Bedrock, Google Vertex AI and Microsoft Azure AI Foundry
A simple guide for business leaders to the three major AI platforms: where each excels and how to choose.
Read article →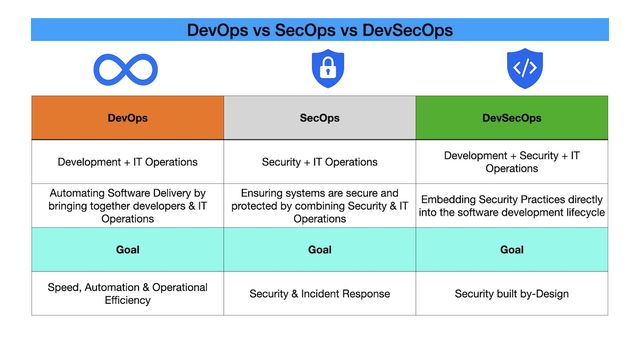
DevOps vs SecOps vs DevSecOps — What’s the Real Difference?
Three terms that sound alike and overlap, explained simply: what each means, who works in them and what each aims for.
Read article →
What AI IS — A Simple Guide for Solution Providers
Seven roles a product can play in the AI ecosystem, from AI-powered to AI-secured, so solution providers can position clearly.
Read article →
What AI Is NOT — Clearing the Confusion Around Today’s AI Landscape
AI is not a product, a platform, an application, a strategy or a magic wand. It is a capability that makes all of them better.
Read article →
Why Agentic AI + Identity Compromise Is Reshaping the Global Threat Landscape
In 2026, agentic AI and stolen identities drive major breaches. What it means for security leaders in the GCC and beyond.
Read article →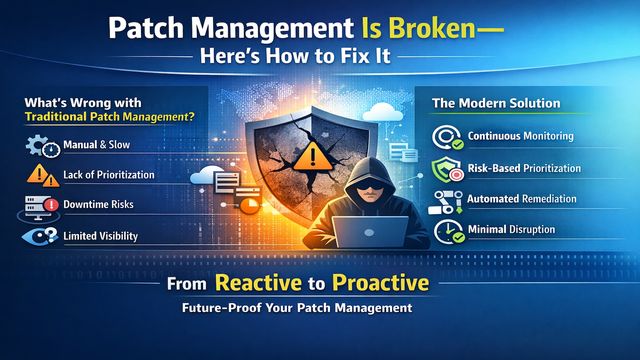
Why Patch Management Needs a Rethink in Today’s Cybersecurity Landscape
Legacy patching is manual, slow and blind to risk. A risk-driven, automated approach turns patching from a chore into a strategic advantage.
Read article →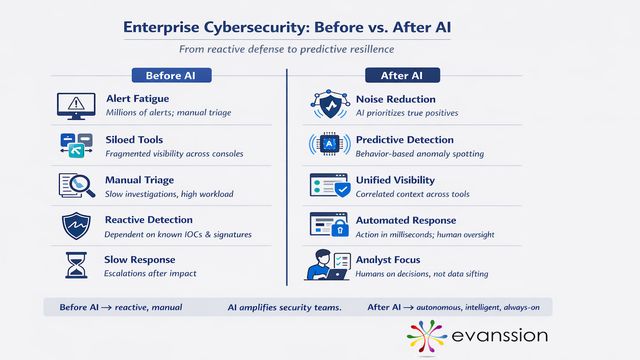
A Look at an Enterprise Cybersecurity Scenario: Before and After AI
A side-by-side view of the SOC before and after AI: alert fatigue, siloed tools and slow response versus predictive detection and autonomous action.
Read article →
Why Cybersecurity Distribution Needs a Value-Added Approach in 2026
Customers in the GCC no longer want only products. Why distribution in 2026 has to add consulting, presales, training and managed services.
Read article →
Harnessing the Power of the Crowd
Combining a global network of ethical hackers with AI-assisted triage to move from periodic testing to continuous, community-powered defense.
Read article →
Why Technology Scales Only When Difference Is Respected
Modern systems do not break because they lack intelligence. They break because they ignore difference, and boundaries are what let them scale.
Read article →
AI-Powered SOC (a.k.a. “Autonomous SOC”): From Reactive Noise to Proactive Defense
How an AI-powered, autonomous SOC cuts alert noise and moves security operations from reacting to anticipating.
Read article →
December Holiday Season & Cyber Risk: Why the Pressure Rises
Attacks rise during holiday periods just as teams wind down. A practical pre-holiday checklist for security and business leaders.
Read article →
Beyond AI Basics: The Next Frontier for Power Users
For people who have mastered the AI basics: moving from content to ecosystems, local models to custom intelligence, and automation to orchestration.
Read article →
Why Network Detection and Response Is the Missing Piece in Cybersecurity
Firewalls, EDR and SIEM leave blind spots in encrypted traffic and lateral movement. How NDR closes the gap.
Read article →
Why GRC Is No Longer Optional — And How the Right Platform Can Make All the Difference
Governance, risk and compliance has moved from a back-office task to a business necessity. What the right platform changes.
Read article →
Why SaaS Security Needs a Rethink in the Age of AI
AI is changing how SaaS applications are used and abused. Why traditional SaaS security falls short and what to rethink.
Read article →
Cybersecurity Readiness Demands Real-World Simulation—Not Just Strategy
Tools alone do not win battles. How cyber simulation platforms build people, process and technology readiness before a real attack.
Read article →
AI Readiness Self-Assessment
A 10-question quiz to find out where your organization is on the AI journey, with a scoring guide and quick wins for any score.
Read article →
How to Make the Most of GITEX: A Human-Centric Guide for Partners and Customers
Why people come to GITEX, what actually sticks with them, and practical tips for visitors and exhibitors.
Read article →
Why Threat Modeling is the Missing Link in Enterprise Cybersecurity Strategy
Threat modeling finds design flaws before attackers do. What it is, what it saves, and how it helps both security teams and business leaders.
Read article →
From Web Security to AI Security: Same Principles, New Frontier
URL filtering, CASB and WAF each have an equivalent in AI security. Map your existing web controls to the new frontier.
Read article →
The Hidden Peril of Over-Transparency in AI: When Explainability Becomes a Vulnerability
Explainability builds trust, but exposed reasoning gives attackers a map. Three principles for balancing transparency with security.
Read article →
AI in the Enterprise: The Double-Edged Sword of Innovation and Cyber Risk
Nine cybersecurity threats enterprises face as they adopt AI, from data leakage and prompt injection to shadow AI, and how to prepare.
Read article →Subscribe
Get new articles and event invitations by email.